Barracuda CloudGen Firewall Secure Access Concentrator for Microsoft Azure
Protecting your Digital Assets in Microsoft Azure
Overview:
 Growth in cloud computing capabilities and services has driven more data into places where traditional IT security measures cannot reach; specifically, data centers not owned by your corporate IT group. The Barracuda CloudGen Firewall F-Series provides centralized management and highly secure, encrypted traffic to, from, and within Microsoft Azure deployments.
Moving your IT Infrastructure to the Cloud? Utilizing Microsoft Office 365? Running on Microsoft Azure?
Barracuda Networks is your partner for various kinds of deployments in Microsoft Azure. We understand your IT needs and we’re acknowledged as “Microsoft Partner – Gold Application Development.” We are also “Microsoft Azure Certified.”
Barracuda Networks and Microsoft Azure
Barracuda Networks was the first Microsoft Azure Certified Security Solution Provider. The Microsoft Azure Certification assures that the Barracuda Solutions have been tested for readiness and compatibility with Microsoft Azure public cloud, Microsoft Cloud Platform hosted by service providers through the Cloud OS Network, and on-premises private cloud Windows Server Hyper-V deployments.
The Microsoft Azure Certification brings customers several benefits
- Time of deployment is cut by 50-80%
- Ease of deployment increased by 90%
- Deployment bandwidth requirements are reduced to near-zero
- Current and future Barracuda on Microsoft Azure products allow both evaluation and purchased licenses at deployment time
Microsoft works closely with Barracuda engineering, solutions architects and sales teams to create a great customer experience and make it easy for customers to leverage the Barracuda CloudGen Firewall, Barracuda Spam Firewall and Barracuda Web Application Firewall to move their applications into the Azure cloud securely.
The Barracuda Spam Firewall and Barracuda Message Archiver offer best-of-breed email management, archiving, and security for organizations utilizing Microsoft Office 365. And there is more to come – stay tuned and learn about the latest innovations from Barracuda Networks and Microsoft Azure.
Moving Your Physical Data Center to the Cloud?
Get Secure Connectivity with Visibility and Control with the industry's most advanced next-generation firewall solution for Microsoft Azure. The Barracuda CloudGen Firewall ensures highly secure, encrypted traffic from, to, and within Microsoft Azure, providing secure remote and site-to-site access, and centralized management.
The growth in cloud computing capabilities and services has driven more data into places where traditional IT security measures cannot reach - into data centers not owned by your corporate IT group. The Barracuda CloudGen Firewall provides centralized management and highly secure, encrypted traffic to, from, and within Microsoft Azure deployments. Securing applications and data in Microsoft Azure is far easier with tools that are dedicated to the task. Deploying the Barracuda CloudGen Firewall in the cloud is very similar to running local network firewalls, and provides the advantages of common policy enforcement and distributed security management in a hybrid-IT environment. It provides next-generation firewalling and secure remote access to Microsoft Azure. It enables organizations to deploy sophisticated multi-zone network architecture in Microsoft Azure, just like their on-premises networks.
By using the proprietary high-performance VPN protocol extension TINA, the Barracuda CloudGen Firewall deployment enables secure high-speed site-to-site and client-to-site connectivity between on-premises networks and mobile-user devices, as well as connectivity between VNETs in Microsoft Azure. Best of all, it features the industry's best centralized management, ensuring highly scalable and fault tolerant network infrastructure required by today’s users, without the management overhead. The Barracuda NextGen Control Center adds a powerful and intuitive centralized management portal that makes it extremely simple to deploy, configure, update, and manage multiple units from a single location, while also providing comprehensive, real-time network visibility and reporting.
The Barracuda Advantage
- Quick rollout
- Comprehensive reporting
- Highly scalable
- Fully compatible with Microsoft Azure
Product Spotlight
- Powerful next-generation network firewall
- Advanced Threat Detection
- Built-in web security and IDS/IPS
- Full application visibility and granular controls
- Centralized management of all functionalities
- Template-based and role-based configuration
Securing the Internet of ThingsThe Barracuda CloudGen Firewall F-Series is designed and built from the ground up to provide comprehensive, next-generation security while being simple to deploy and maintain, and highly scalable. Need to connect micro-offices, point of sales and machine-to-machine business? With the F-Series you're all set! |
|
Easy to setup and maintain: SC1The Secure Connector (SC1) is a hardware appliance purposebuilt to be an on-premises connectivity device that ensures high-performance and tamper-proof VPN connections to protect the data flow and, thus, guarantee data continuity. |
|
Bundling the data stream: SACThe Secure Access Concentrator is the collecting point for the data stream. This fully fledged CloudGen Firewall acts as VPN gateway for the SC1 deployments. SACs can be run on VMware, Hyper-V, XenServer, or KVM environments as well as directly in Microsoft Azure. |
|
Grows with your needsIntegration within the Barracuda NextGen Control Center architecture ensures that your deployment can grow with your needs without technical or financial trapdoors. The template-based configuration ensures easy rollout of additional devices and maintain compliance. |
Deployment:
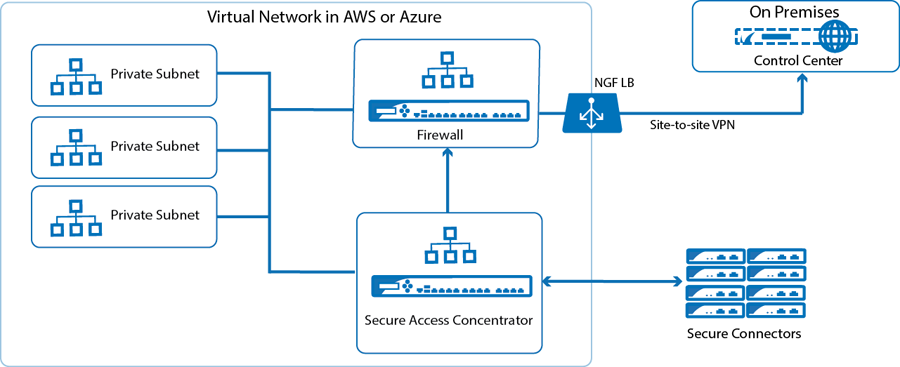
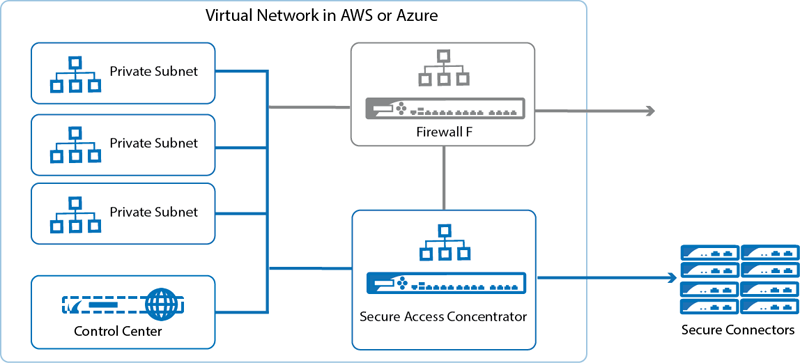
The Secure Access Concentrator can be deployed in Azure and AWS if your FSCs are geographically dispersed and/or your backend systems hosted in Azure and/or AWS. The FSAC connects your Secure Connectors with your cloud resources and allows you to monitor the traffic between the FSC and the private subnets. If VPN connectivity is required, the FSAC is used in combination with an F-Series Firewall. You have two options for setting up the Secure Access Concentrator. The deployment steps are the same as the steps required for an on-premises FSAC.
FSAC and F-Series Firewall in the Public Cloud, Control Center located on-premises
In this scenario, the FSCs connect to the public IP address of the FSAC. In Azure, traffic to the backend subnets is routed over the F-Series Firewalls; in AWS, the FSAC connects directly to the backend subnets. The F-Series Firewall handles the VPN tunnels to the on-premises networks. Configuration data from the FSAC to the Control Center is sent through this site-to-site tunnel.
FSAC, F-Series Firewall, and Control Center in Azure and Amazon Web Services
The client connects to the public IP address of the FSAC. Traffic to the backend is routed either through the optional F-Series Firewalls, or directly to the backend subnets. The FSC can connect directly to the Control Center, which is located in another subnet. In Azure, the FSAC can also secure the traffic between the different backend subnets. An F-Series Firewall is required for site-to-site VPN connections to your on-premises networks.
Model Comparison:
| SAC Editions1 | SAC400 | SAC610 | SAC820 |
|---|---|---|---|
| Number of Protected IPs | unlimited | unlimited | unlimited |
| Allowed Cores | 2 | 4 | 8 |
| Max. number of VPN Connections | 500 | 1,200 | 2,500 |
| Firewall & VPN Throughput | 1 Gbit/s | 2 Gbit/s | 4 Gbit/s |
| Firewall | |||
| Application Control2 | |||
| IPS2 | |||
| Dynamic Routing | |||
| VPN3 | |||
| SSL Interception | |||
| Web Filter | |||
| Malware Protection4 | Optional | Optional | Optional |
| Advanced Threat Detection4,5 | Optional | Optional | Optional |
1 The Barracuda CloudGen Firewall F-Series SAC virtual image covers all editions.
2 Requires a valid Energize Updates subscription.
3 Barracuda CloudGen Firewall F-Series SAC editions include as many VPN licenses as the number of protected IPs. VPN clients with an active connection to the Barracuda CloudGen Firewall F-Series SAC are counted towards the protected IP limits.
4 Including FTP, mail and Web protocols.
5 Requires a valid Malware Protection subscription.
Technical Specs

Firewall
- Stateful packet inspection and forwarding
- Full user-identity awareness
- Intrusion Detection and Prevention System (IDS/IPS)
- Application control and granular application enforcement
- Interception and decryption of SSL/ TLS encrypted applications
- Antivirus and web filtering in single pass mode
- SafeSearch enforcement
- YouTube for Schools support
- Denial of Service protection (DoS/DDoS)
- Spoofing and flooding protection
- ARP spoofing and trashing protection
- DNS reputation filtering
- TCP stream reassembly
- NAT (SNAT, DNAT), PAT
- Dynamic rules / timer triggers
- Single object-oriented rule-set for routing, bridging, and routed bridging
- Virtual rule test environment

Hypervisor and Public Support (for SAC and NextGen Control Center)
- VMware
- Hyper-V
- XenServer
- KVM
- Microsoft Azure

Intrusion Detection & Prevention
- Protection against exploits, threats and vulnerabilities
- Packet anomaly and fragmentation protection
- Advanced anti-evasion and obfuscation techniques
- Automatic signature updates

Advanced Threat Detection
- Dynamic, on-demand analysis of malware programs (sandboxing)
- Dynamic analysis of documents with embedded exploits (PDF, Office, etc.)
- Detailed forensics for both malware binaries and web threats (exploits)
- Support for multiple operating systems (Windows, Android, etc.)
- Flexible malware analysis in the cloud

VPN
- Secure site-to-site
- Supports AES-128/256, 3DES, DES, Blowfish, CAST, null ciphers

High Availability
- Active-passive
- Transparent failover without session loss
- Network notification of failover
- Encrypted HA communication

Central Management Options
- Barracuda NextGen Control Center
– Unlimited SACs and SC1s
– Support for multi-tenancy
– Multi-administrator support & RCS

Protocol Support
- IPv4
- BGP/OSPF/RIP
- VoIP (H.323, SIP, SCCP [skinny])
- RPC protocols (ONC-RPC, DCE-RPC)
- 802.1q VLAN
Support Options

Barracuda Energize Updates
- Standard technical support
- Firmware updates
- IPS signature updates
- Application control definition updates
- Online web filter
Security Options
- Advanced Threat Detection
- Malware Protection
Pricing Notes:
- Pricing and product availability subject to change without notice.
List Price:
Our Price: $832.20
List Price:
Our Price: $2,565.00
List Price:
Our Price: $9,690.00
List Price:
Our Price: $112.86
List Price:
Our Price: $323.76
List Price:
Our Price: $1,425.00
List Price:
Our Price: $131.10
List Price:
Our Price: $338.58
List Price:
Our Price: $1,539.00
List Price:
Our Price: $169.86
List Price:
Our Price: $490.20
List Price:
Our Price: $1,995.00