Barracuda Backup for Amazon Web Service
Protecting your Digital Assets in Amazon Web Services
Sorry, this product is no longer available, please contact us for a replacement.
 Overview:
Shared Security with Barracuda on Amazon Web Services
Amazon Web Services offers a broad set of secure compute, storage, application, and deployment services that help organizations to move faster, scale applications, and lower IT costs. However, since you are still responsible for protecting your own AWS-based assets you need security that can complement the AWS shared security model. That’s where Barracuda can help.
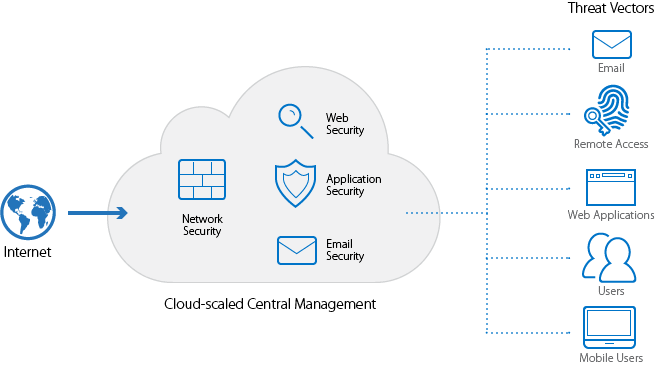
In the cloud, companies still need to protect their business resources, also known as network threat vectors—company email, web applications, network perimeter, remote access, mobility, and users. While threat vectors remain constant, attack surfaces are always changing; these include physical, virtual, and cloud. What’s required is powerful security for applications, network, web, and email. Barracuda understands your IT needs and provides best-of-breed solutions for firewalling, load balancing, web application security, and email security on Amazon Web Services.
Barracuda and Amazon work well together - we both want to make IT simple while delivering comprehensive, in-depth security.
"We had security gaps in our departments. We looked around, did some research and found exactly what we wanted in Barracuda. That’s about the whole story."
Sergey Rodovinsky
VP of Technology, IRIS Solutions
Barracuda Solutions Available in AWS GovCloud Region
Barracuda’s AWS-enabled products are available in AWS GovCloud – an isolated AWS region designed to allow US government agencies, nonprofits and educational institutions, and private sector companies with heightened security needs to move sensitive workloads into the cloud. AWS GovCloud helps organizations address very specific compliance requirements including those posed by the US International Traffic in Arms Regulations (ITAR), FedRAMPSM and DoD CSM Levels 1-5 specifications. Barracuda provides the additional layer of real-time security for applications built on this AWS GovCloud environment, allowing customers to completely protect their mission critical workloads. Customers can now leverage best-in-class Barracuda security and storage solutions with their applications strengthening their overall privacy and data protection policies.
Application Security:
Comprehensive Security for Application Protection on Amazon Web Services
The Barracuda Web Application Firewall for AWS is a scalable security solution that protects applications from targeted and automated attacks. Customers are able to:
- Protect web applications from data breaches, defacement, OWASP Top-10 Attacks, application layer DDoS and other attack vectors
- Receive automatic updates with defense against new threats and vulnerabilities with real-time protection
- Use strong authentication and access control capabilities to ensure security and privacy – restrict access to sensitive applications or data
- Ability to bootstrap and auto scale as required with automated and clustered deployments using CloudFormation templates.
- Available on the AWS marketplace as a single AMI or as a CloudFormation Template via the AWS Marketplace support for Clusters and AWS Resources
Barracuda’s simplified IT model gives your organization an easy to use and affordable security solution. Companies of all sizes can enjoy total application security without learning, configuring, or managing complex technology.
Deploy Barracuda Web Application Firewall on AWS
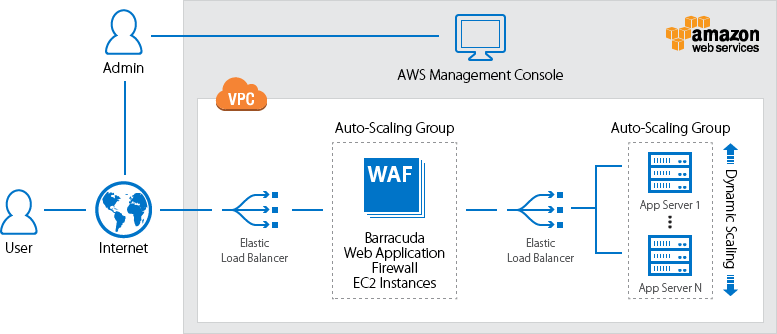
Take advantage of auto-scaling by deploying the Barracuda Web Application Firewall clusters in an auto-scaling group on AWS.
- Build a multi-tier redundant architecture that allows you to independently scale each tier based on your requirements.
- Automatically scale based on metrics or a schedule to meet business needs. (An example of metric based scaling is an increase in traffic load; an example of scheduled scaling is to meet a planned traffic increase during a sale or holiday.)
Powerful Support for AWS Services
As an AWS Security Competency Certified Partner, the Barracuda Web Application Firewall supports a variety of AWS Services enabling customers to fully leverage the power of their AWS environment. The support includes the ablity to launch a dynamically scaling cluster of Barracuda WAF’s using AWS CloudFormation Templates. In such deployments, the Barracuda Web Application Firewall integrates with CloudWatch for performance monitoring and scaling alarms. All deployments are within an AWS Virtual Private Cloud (VPC) and secured using AWS Identity and Access Management (IAM).
The Barracuda Web Application Firewall fully supports deployment with the AWS Elastic Load Balancer. The AWS ELB can be deployed both upstream and downstream of the Barracuda Web Application Firewall auto scaling cluster. This ensures that the backend application servers can auto scale independently of the Barracuda Web Application Firewall cluster.
The Barracuda Web Application Firewall is available across various AWS regions and marketplace options. It is available on the AWS GovCloud region, which is a secure and isolated AWS Region desgned for US governement and related entities with stringent reglatory and compiance requirements. The Barracuda Web Application Firewall is also available on the AWS Marketplace Support for Clusters and AWS Resources programs. This allows customers to launch the Barracuda Web Application Firewall via a Cloud Formation Template directly from the marketplace page.
Publish SharePoint Securely with the Barracuda Web Application Firewall
Amazon Web Services provides a number of tools and processes to help you move critical business applications like SharePoint to the cloud. Capitalize on the AWS shared security responsibility model by implementing your own tools to secure SharePoint deployments in the cloud, especially when providing access to remote users via the Internet.
The Barracuda Web Application Firewall running on AWS helps secure your SharePoint deployment to the cloud, including protection from web-based attacks, data leak prevention, denial of service protection, and user access controls. Many AWS customers have addressed these and other challenges related to dynamic scaling, load balancing as well as federating their corporate directory for accessing SharePoint with a Barracuda Web Application Firewall on AWS.
Discover Existing Web Application Vulnerabilities
Web application development is a dynamic process, and with features to implement and timelines to meet, security vulnerabilities will inevitably occur. The Barracuda Vulnerability Manager is a non-invasive, web-based scanning tool that quickly discovers application security flaws such as those on the OWASP Top 10, including SQL injection, cross-site scripting, and others. It is provided at no charge by Barracuda. The detailed output of the scan lists all vulnerabilities discovered, ranks them from most to least critical, and provides additional insights to help you address them.
Centrally manage multiple Barracuda WAF units
The Barracuda Application Security Control Center is the centralized management system that allows administrators to manage multiple geo-dispersed Barracuda Web Application Firewalls with varying configurations from a single console.
- Single pane of glass view of all connected Barracuda WAF units
- Built-in templates make it easy to configure rapidly
- Deploy in a variety of virtual and cloud environments
Network Security:
Secure Your Network Perimeter on Amazon Web Services
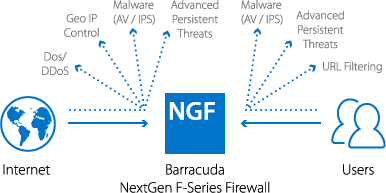
Get secure connectivity with visibility and control by using the Barracuda CloudGen Firewall F-Series, the industry's most advanced next-generation firewall solution for deployments on Amazon Web Services. The growth in cloud computing capabilities and services has driven more data into places where traditional IT security measures cannot reach, like data centers not controlled by your corporate IT group.
Barracuda CloudGen Firewall F-Series includes:
- Advanced Threat Detection
- Quality of Service capabilities (QoS)
- Full application visibility and user awareness
- Intrusion Detection and Prevention System (IDS/IPS)
- Antivirus and URL filtering
- Secure remote access to Amazon Web Services
- Granular security and policy management
Barracuda Secure Connectivity
Customers deploy the Barracuda CloudGen Firewall F-Series on AWS because it delivers
- Endpoint to endpoint (not network-to-network) connectivity
- Dynamic Address Support
- Highly robust and fast reconnecting VPN
- Roaming- and NAT friendly clients for Microsoft, Mac OS, and Linux
- Central management of all capabilities with NextGen Control Center
Deploy Secure Multi-Tier Network Architectures Using Barracuda CloudGen Firewall F-Series on AWS
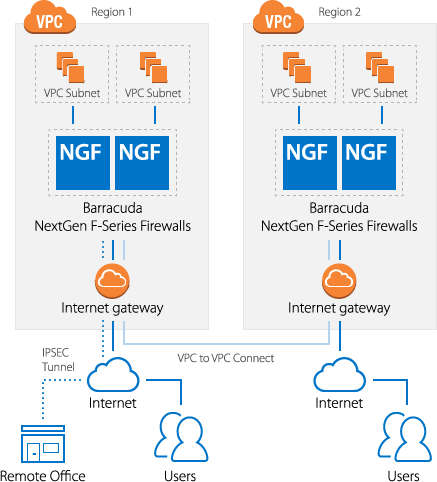
The powerful F-Series Firewall enables organizations to deploy sophisticated multi-zone network architecture in the cloud, just like their on-premises networks. By using the proprietary high-performance VPN protocol extension TINA (Transport Independent Network Architecture), the Barracuda CloudGen Firewall F-Series can securely extend multi-tier deployments beyond a single datacenter by building high speed VPN tunnels across AWS Regions.
- Enforcement of outbound access control list
- Centrally managing on-premises and AWS deployed NG Firewalls
Deploying a Barracuda CloudGen Firewall F-Series on AWS
Deploying the Barracuda CloudGen Firewall F-Series in the cloud is very similar to running local network firewalls, and provides the advantages of common policy enforcement and distributed security management in a hybrid-IT environment.
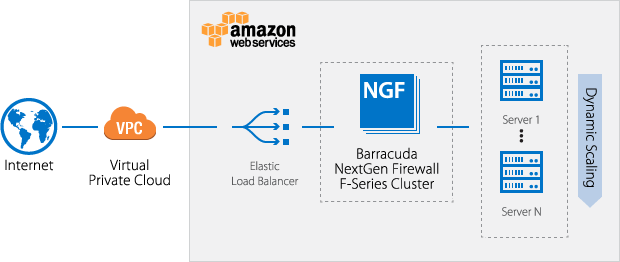
Secure Remote Access with Barracuda CloudGen Firewall F-Series
Barracuda CloudGen Firewall F-Series is an enterprise-class firewall system available as a virtual appliance for both public and private clouds as well as a hardware appliance of various sizes. One of its key components is a flexible and robust VPN service supporting secure site-to-site and client-to-site connections using several different tunnelling protocols.
Barracuda NextGen Control Center
Advanced Traffic Control and Management for Distributed Firewalls
Centralizing all management across many different next-generation firewalls and remote-access users, the Barracuda NextGen Control Center enables administrators to manage and configure security, content, traffic management, and network access policies from a single interface.
This solution is designed for companies who have implemented multiple distributed firewalls, and streamlines management as well as centralizing policy distribution and other global functions:
- Allows creation of re-usable objects for any configuration entry imaginable, such as IP address, DNS names, policies, etc.
- Centralizes software updates for all managed CloudGen Firewall instances
- Provides a “drag & drop" VPN Graphical Tunnel Interface Editor to streamline creation and management of VPN tunnels
Application Delivery:
Enhance Application Performance on Amazon Web Services with Barracuda Load Balancer ADC
When hosting web applications on Amazon Web Services, it’s important for your users to see the same or better performance as they would if the application was deployed within a local data center. The Barracuda Load Balancer ADC provides rich Layer 7 application management and delivery features on AWS, and offers proven technology that has blocked more than 11 billion real-world attacks combined with outstanding ease of use with pre-built application templates for rapid deployment.
Customers deploy Barracuda Load Balancer ADC for:
- Enabling high availability across multiple sites, and speed disaster recovery with Global Server Load Balancing
- Content routing and rewriting to enable full control of application traffic
- Restricting application access to ‘known users’ only, providing protection and preventing loss of data
- SSL offloading, TCP pooling, and compression to accelerate application delivery
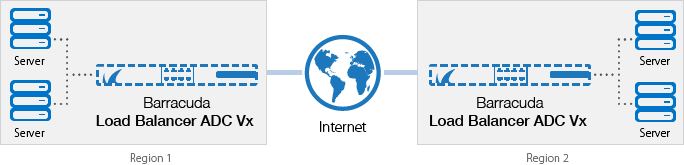
Deploy the Barracuda Load Balancer ADC on AWS
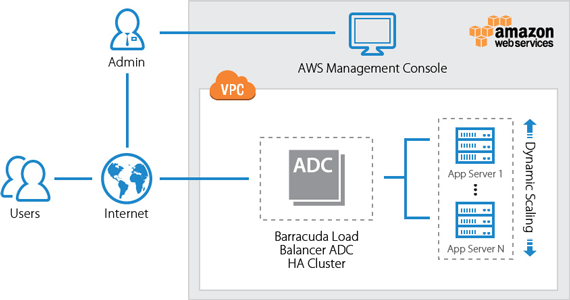
Take advantage of advanced load balancing and application security features of the Barracuda Load Balancer ADC by deploying it in a High Availability (HA) cluster on AWS. The deployment can be fully automated by using AWS CloudFormation Templates and the Barracuda Load Balancer ADC's bootstrapping capabilities.
Email Management:
Migrating Your Email Infrastructure to Amazon Web Services?
Be sure to move your Email Security solution with it—Barracuda Email Security & Email Management on AWS.
Barracuda’s email solutions optimize email deployments on AWS by strengthening security with real-time threat protection and extending email availability for this critical application. Barracuda’s security and storage products give organizations peace of mind in having complete control of their cloud-based email infrastructure.
Protect Your Email Infrastructure with the Barracuda Email Security Gateway for Amazon Web Services
Email servers that reside in the cloud deserve the same level of comprehensive security as email servers that reside on premises. That’s why it’s advantageous to use Barracuda’s proven email security solution that includes the same technology and has the same suite of features as our award-winning hardware appliance.
Barracuda Email Security Gateway delivers comprehensive email security by providing:
- Protection for inbound and outbound email traffic with advanced threat protection features
- Real-time protection against new threats
- Granular DLP and encryption capabilities
- Blocks for confidential or sensitive information from being leaked
- Cloud Protection Layer for email continuity
Key Use Cases
- Prevent zero-day and targeted attacks from jeopardizing your email users
- Ensure sensitive information stays within the organization
- Provide additional layer of redundancy for business-critical apps such as email
Barracuda Message Archiver
Cloud-based email services like Office 365 are an attractive solution for organizations looking to provide optimum email service for their users at predictable costs.
The Barracuda Message Archiver enhances user productivity and reduces cost and risk by simplifying user access, email management, and eDiscovery/compliance.
- Offers customizable email retention rules
- Allows organizations to designate auditors to apply litigation holds
- Provides an easy and secure way to archive mail from cloud-based email services like Office 365
Pricing Notes:
- Pricing and product availability subject to change without notice.